I had the opportunity to stop in at the Game Hacking Village in their first year at DEF CON 32, and I have to say the village has grown significantly since. For DEF CON 34, the Game Hacking Village was granted more space in a prime location directly across from the Red Team Village. Zetier was a sponsor again this year and made it possible for me to be a Technical Evangelist on more than one front, and I’m excited to talk about what that looked like from my own viewpoint. As is typical for me, much of it was absurd.
First, I’m known as dwangoAC, keeper of TASBot online, and I’ve been with Zetier since late last year. I’ve been in some form of test engineering and security work for over two decades professionally, but in 2013 I started the TASBot community to show our cute robotic mascot playing video games perfectly for charity, helping raise more than $1.5M at Games Done Quick and other charity marathons since.
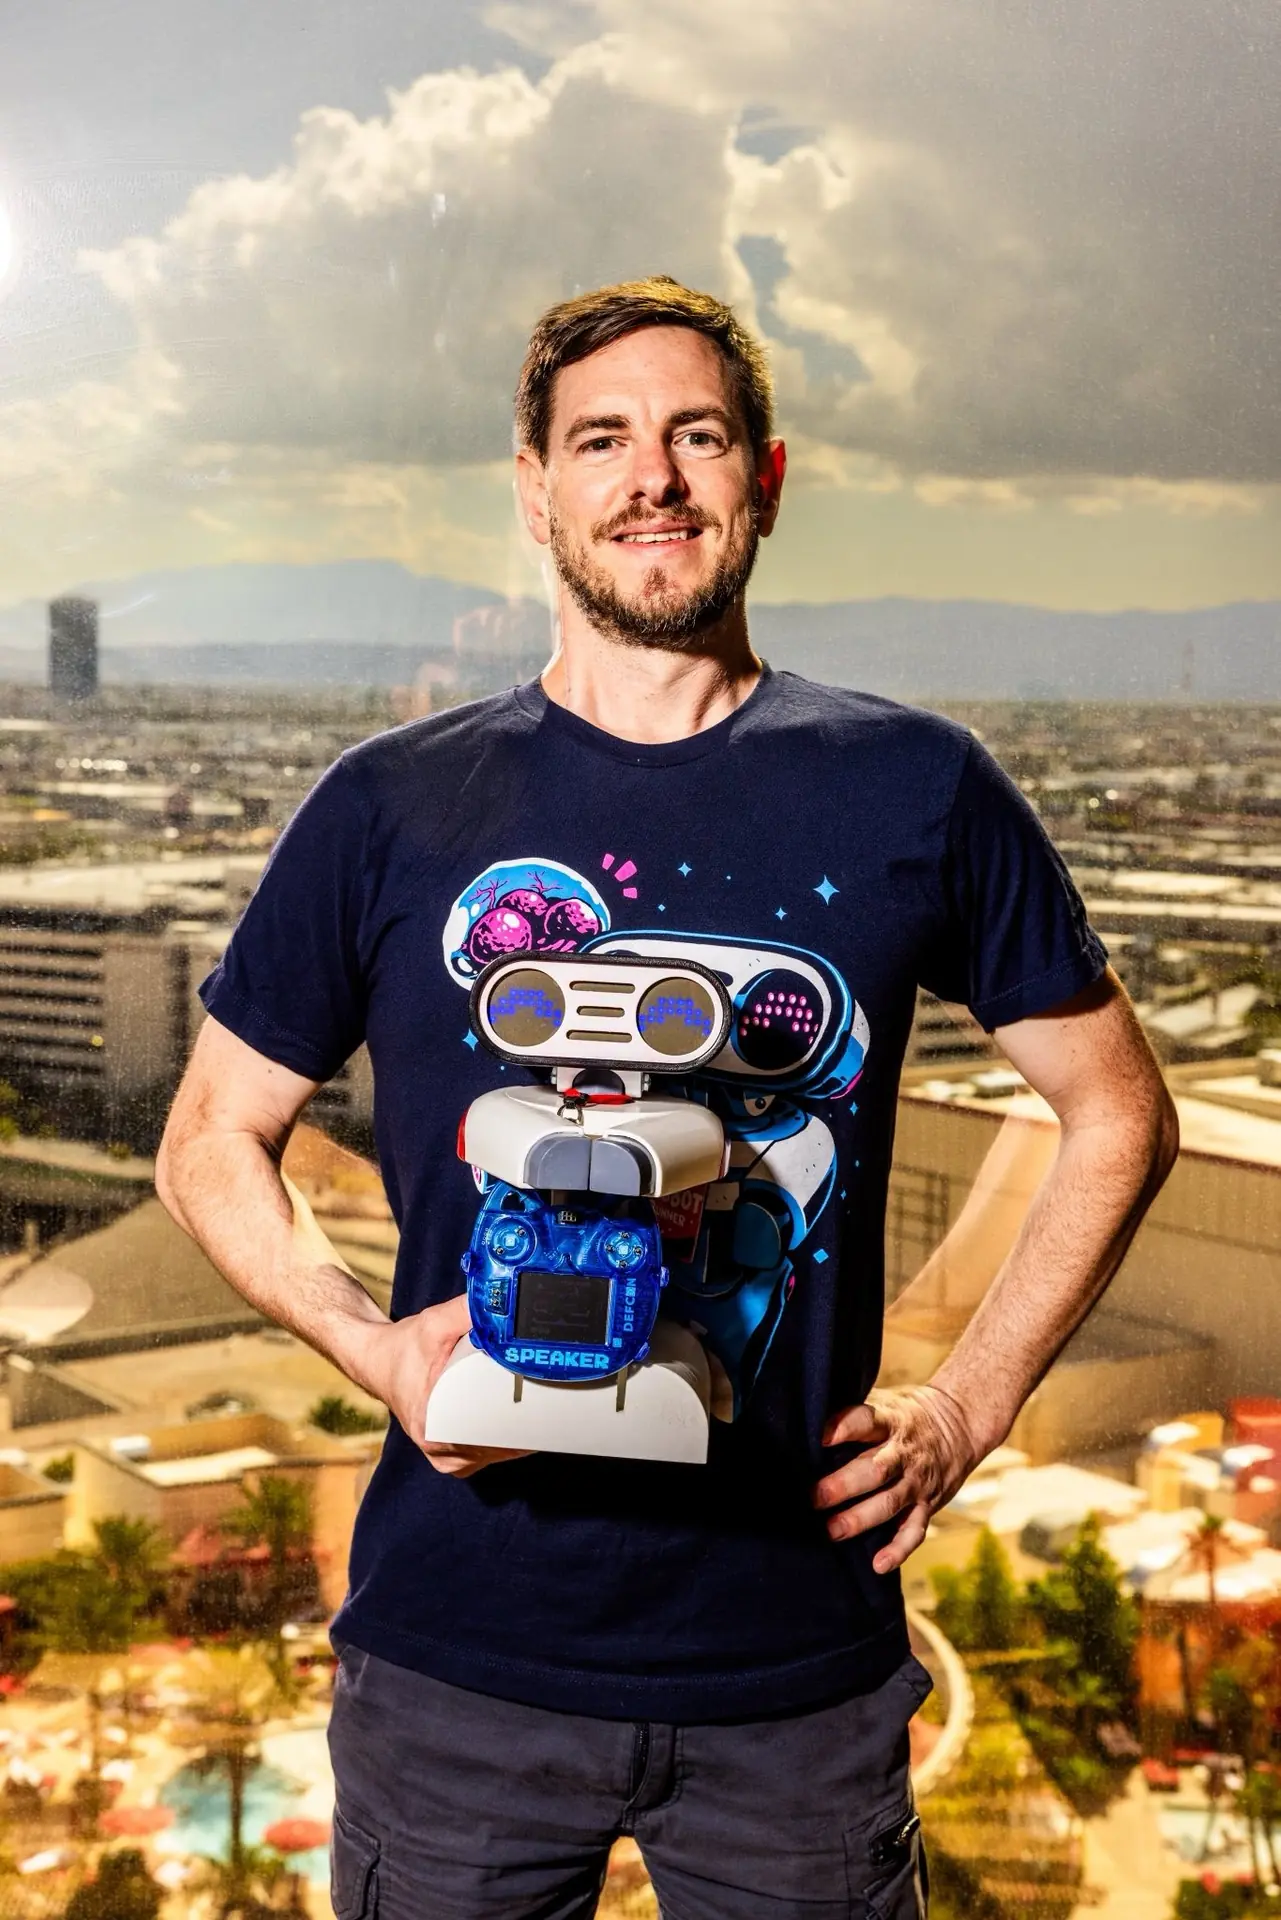
I joined Zetier after the fantastic Speedrunners are Vulnerability Researchers blog post caught my attention as I had previously given a DEF CON 24 talk on the topic, and I’ve long espoused the value of learning vulnerability research in the safety of a classic video game in an emulator. Zetier enabled me to combine my passions at the Game Hacking Village this year, for which I am thankful.
Yes, DEF CON Attendees Jammed My Talk

Overall, I enjoyed presenting my talk “Yes, I Froze an SNES for TASBot” on the creator stage despite some audio interference. I presented statistically significant evidence showing the variance in audio sound processing speed (specifically, the DSP sample rate) from one Super Nintendo console to another has more impact than temperature, diving into the impact it has on speedrunners.
The audience and I experienced the joys of listening to the talk over headsets, and by joys I mean enterprising DEF CON attendees jamming the frequencies resulting in sonic trauma, but I felt I was able to navigate the challenges well enough and I was happy to have such a receptive audience.
DEF CON Disasters, Dispatched
As with most big events, there are always more challenges. DEF CON 34 was plagued with network connectivity issues that impacted the Game Hacking Village CTF, there was a shortage of projectors and screens available for reservation, and there were plenty of badge bodges I could recount over a beverage. Early on we realized I wouldn’t have a screen to work with, so a couple of my colleagues went thrift store hopping and picked up a monitor for me that came in extremely handy for showing off what TASBot can do.
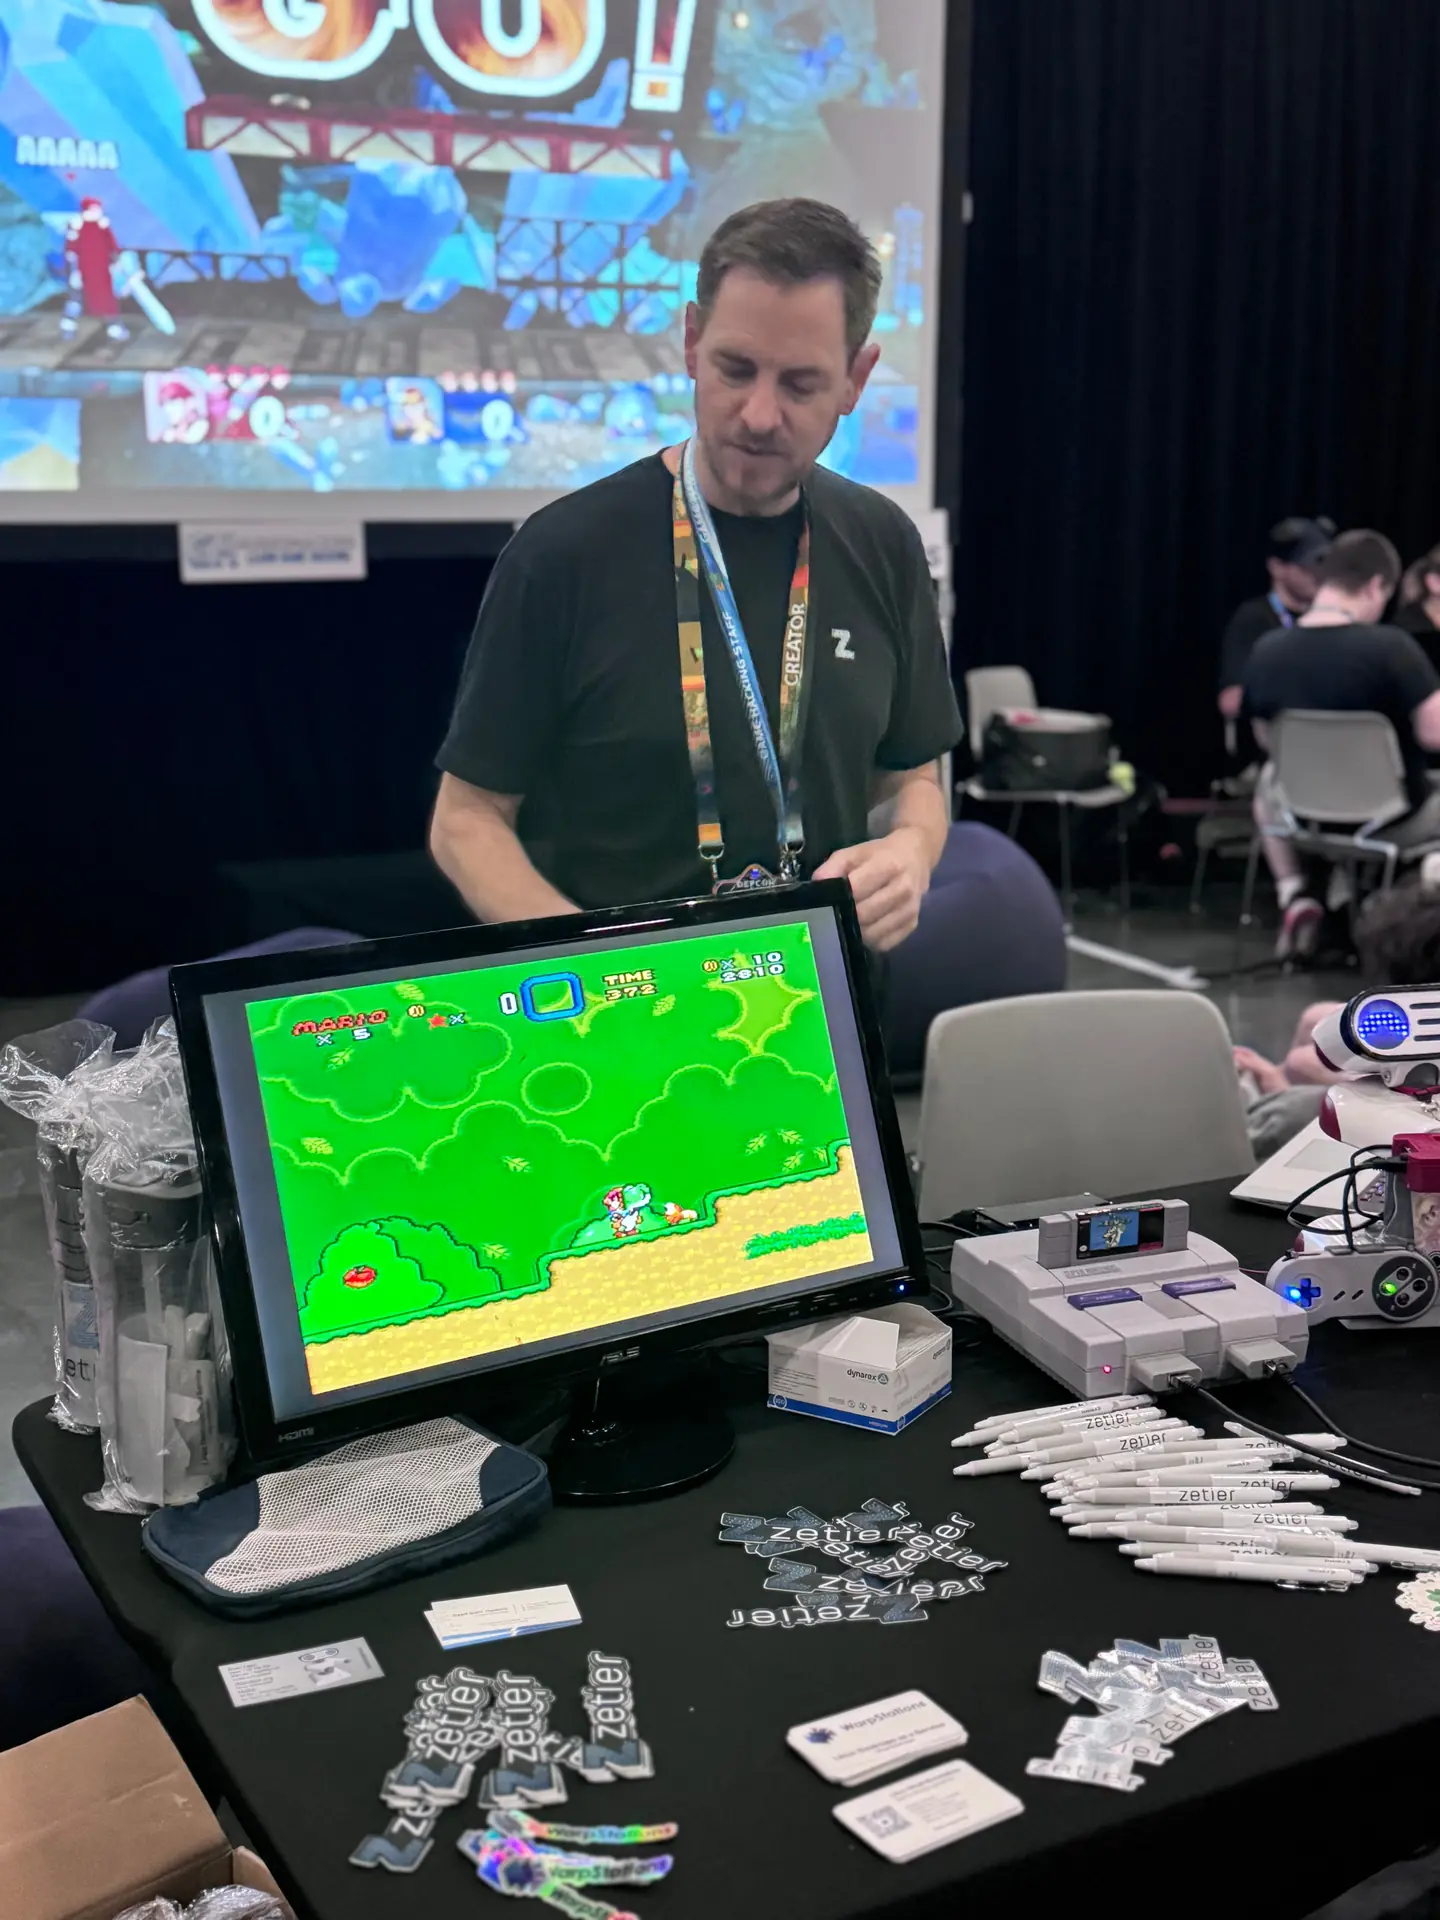
I spent most of my weekend demonstrating how TASBot can play back various Tool-Assisted Speedruns of Super Mario World on said monitor, but more on that in a moment.
Hacking Melee
I was able to take over the main Game Hacking Village chill space projector at various points to allow TASBot to pummel willing participants into the ground on Super Smash Bros. Melee thanks to help from AltF4’s SmashBot (TASBot isn’t any kind of AI or virtual intelligence on his own, but he can buddy up and blink cutely when called upon and AltF4 himself was even present). As was the theme, this involved hacking the game through the use of an Arbitrary Code Exploit (ACE), which allowed us to feed the opponent’s coordinates out of a special memory card adapter connected back to TASBot.
Participants were encouraged to figure out how to hack SmashBot’s logic, with at least one team accomplishing the feat each day. As an added award, I tossed in a TASBot plushie for the winner of the Smash Bros. tournament, and they were happy to receive him.

Super Mario…World?
On the Super Mario World side, I was able to show off how TASBot playing a TAS on a real console is similar to how a player piano plays back the work of a composer; what’s being shown is transformative human art, one button press at a time, and in my case doing it for charity. I was able to demonstrate an ACE inside of Super Mario World that took over the console to allow attendees to play the original Super Mario Bros. along with other ACE fun.
My Zetier colleagues had an opportunity to chat with folks coming to see the commotion while all that was going on, and it was frequently a commotion given how many folks were clustered around TASBot. My colleague Henry later commented “it was impossible to get around because you single-handedly amassed an entire audience every time I was there”.

Game Hacking for Fun and Profit
It was good being able to connect with people over our shared love of vulnerability research and extend invitations to apply for open reverse engineering roles at Zetier. There was more fun had during the Game Hacking Village CTF that Zetier also supported, but that’s a blog post for another day, so stay tuned! All in all, this was the most successful Game Hacking Village event yet, and I for one look forward to being part of next year’s shenanigans.
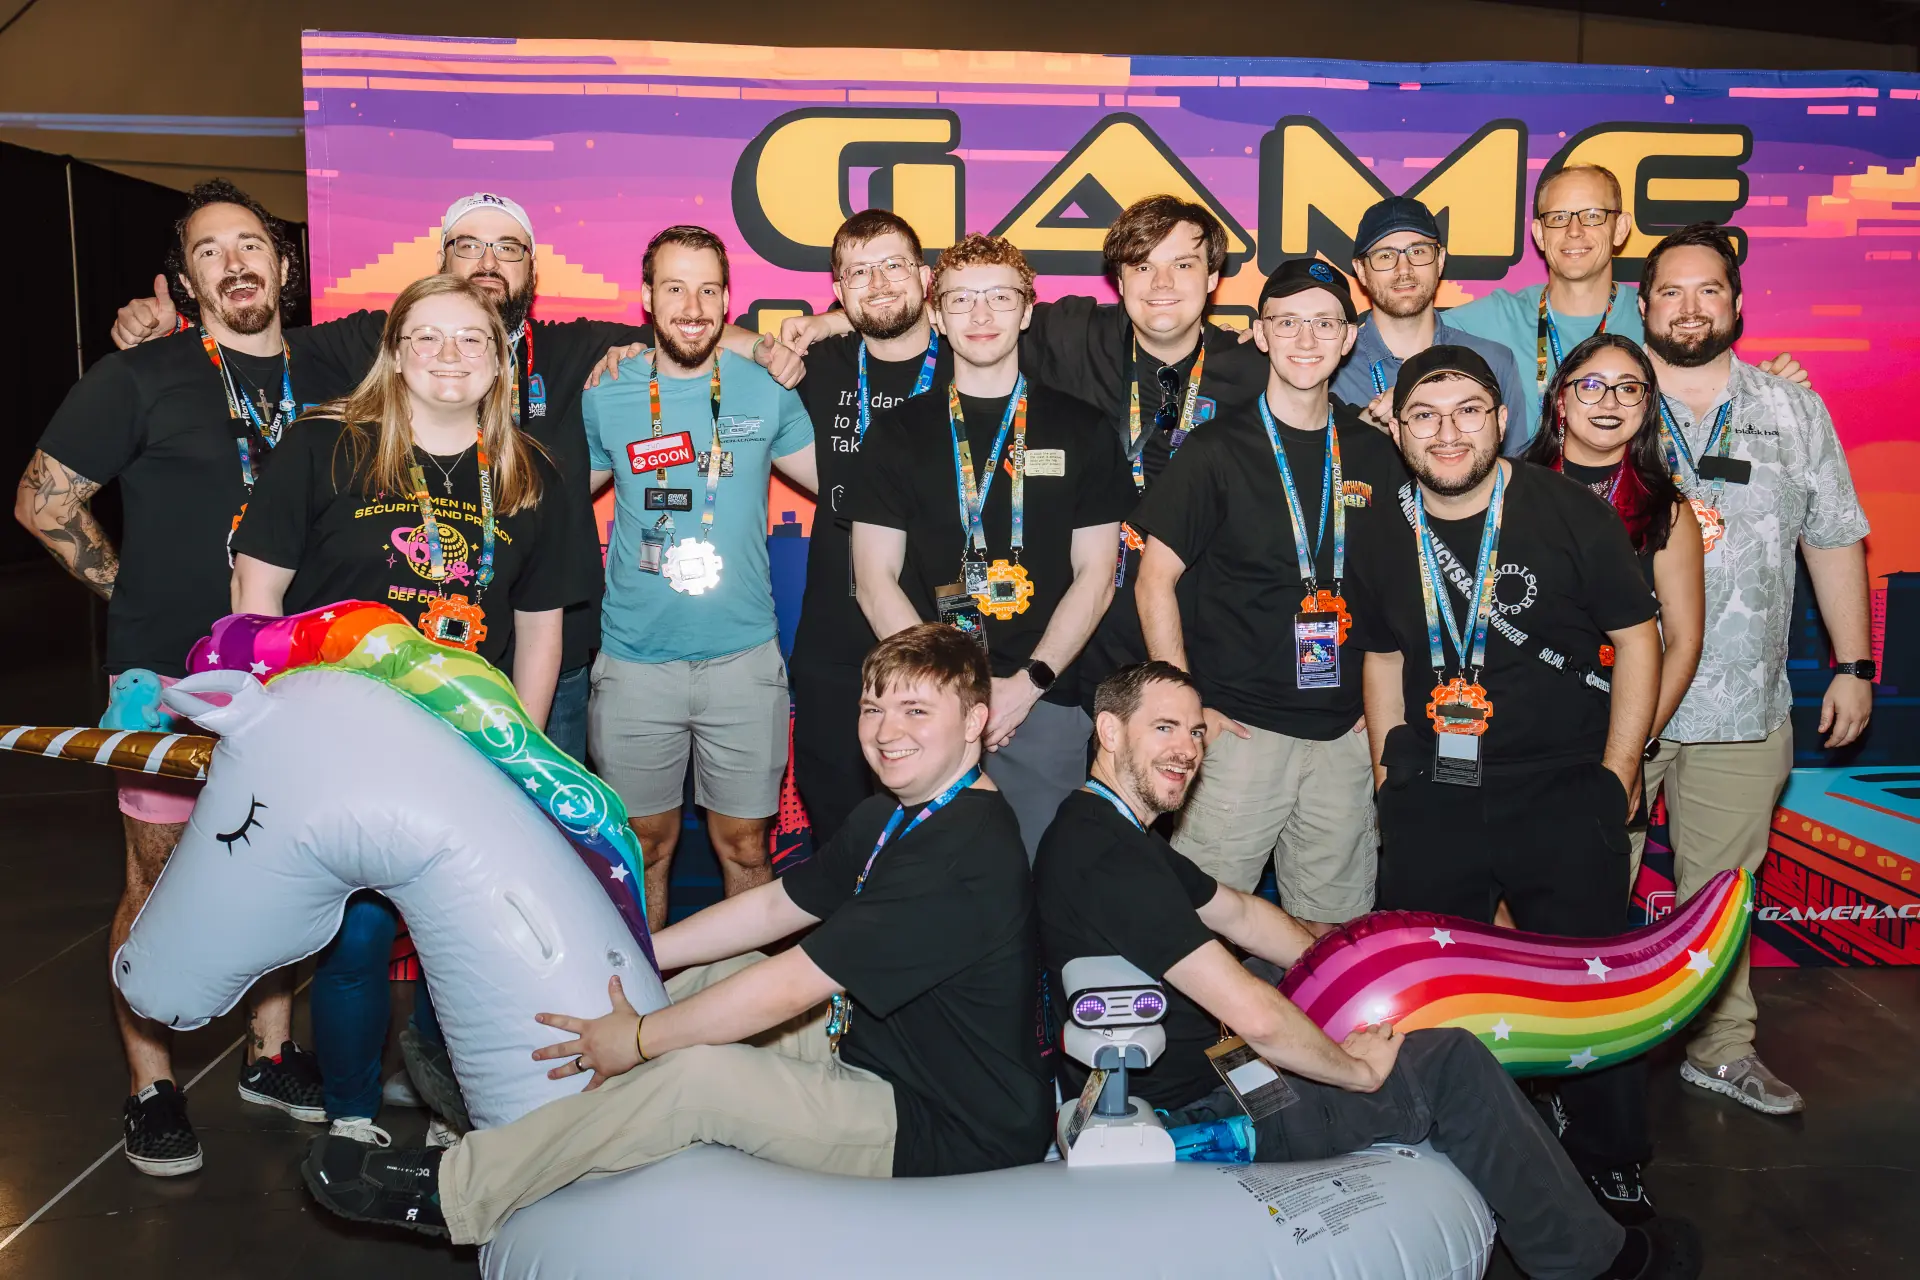
Illustration by Inkinetic Studios, photographs used in accordance with DEF CON media and privacy policy.